Insights
Notes from the practice.
Strategy, governance, cost control, and risk in business terms.
Featured
Public Safety
What to measure in month one of an AI non-emergency line
Colorado Springs and Dane County just published early numbers from AI agents answering their non-emergency lines. A completion rate and a call count are a start, but month one has to measure missed emergencies, handoff quality, and who fixes the failures.
Sep 29, 2026 · 7 min read
AI Governance
What your Texas health system customer will ask about AI disclosure
Two Texas laws put AI disclosure duties on the health care provider, not the vendor. Your health system customer will turn those duties into questions for you, and the answers have to live in the product.
Sep 29, 2026 · 7 min read
AI Governance
A Model That Reads CT Scans Just Shipped With Its Weights. That Is the Guardrail
Alibaba's DAMO Academy open-sourced RADAR, a model that reads abdominal CT scans across 146 findings and beat 23 of 26 radiologists in the study. The interesting part is not the accuracy. It is that anyone can download it and check the claim.
Sep 25, 2026 · 6 min read
Recent
AI Governance
The Agent That Writes Its Own Success Metric Is the One to Watch
Most companies split the decision: the KPI an agent is measured on is an operations call, the tools it can touch is a security call, and different people own each. That split stops working the moment one agent sets its own target, reaches across systems to hit it, and reports that it succeeded. Here is the one-page brief that pulls the three apart.
Sep 24, 2026 · 6 min read
AI Governance
The Three Questions You Can Answer for an Employee and Not for Your Agents
For any person on your payroll you can say what they are allowed to do, on whose behalf, and who approved it. If you cannot answer those three for an agent running in production, you do not have a security gap, you have a governance gap. Here is the one-page inventory that closes it.
Sep 24, 2026 · 6 min read
AI Governance
The FDA is proposing to test your AI the way it tests a physician
A August 2026 FDA discussion paper floats competency-based evaluation for generative AI medical devices: benchmark the deployed product, then confirm clinically. It is not guidance and it is not binding, but it tells you what your risk file will need to say.
Sep 19, 2026 · 6 min read
AI Security
The control blocks the tool and leaves the threat alone
Blocking github.com at the firewall stops nobody and costs your engineers an hour a day. Here is how to tell a control that manages risk from one that manages appearances, and what to replace the theater with.
Sep 19, 2026 · 6 min read
AI Governance
Your shadow AI inventory is stale before you finish it
A one-time discovery sweep gives you a snapshot that decays in weeks, because the AI arrives inside software you already approved. Here is what turns the inventory into a control instead of a spreadsheet with a date on it.
Sep 19, 2026 · 6 min read
AI Governance
Fifty-seven percent is a product requirement, not a compliance finding
A Wolters Kluwer Health survey found 57% of healthcare professionals have encountered or used unauthorized AI at work, and about half said the reason was speed. If you sell into health systems, that number is telling you what your product does not do yet.
Sep 19, 2026 · 6 min read
AI Security
One stolen token, three hours, full cloud admin
Anthropic's threat report describes an escalation from a single developer token to full cloud administrative control in roughly three hours. Nothing in the tradecraft was new. What changed is the clock, and the clock is what your response plan is built on.
Sep 19, 2026 · 6 min read
AI Security
Two products want to decrypt the same traffic. Only one can be first.
When an AI DLP tool lands next to an existing secure web gateway, both need cleartext on the same flow. Interception does not fan out. Here is how to decide the order, and what breaks when you get it wrong.
Sep 19, 2026 · 6 min read
AI Governance
Stop reporting vuln counts to the board and start reporting risk
We reduced open P1s by 15 percent does not survive a follow-up question. Here is a one-page worksheet that turns a finding into a board-defensible risk statement.
Sep 18, 2026 · 6 min read
AI Security
The model retention question that stalls your AI deal in security review
Big buyers are barring commercial AI models over 30-day data retention. Five questions to answer before your security review turns retention into a deal blocker.
Sep 18, 2026 · 5 min read
Public Safety
The Encryption Key Was on the Flock Camera
A recovered Flock ALPR held its encryption key on the device, computer-vision models that detect people, and 21 days of logs covering about 1.6 million images. That is a procurement fact, not a hacking story.
Sep 16, 2026 · 8 min read
Public Safety
The AI on the case file is not the one you bought
The demo is not the risk. The risk is case data already leaving through personal ChatGPT, Gemini, and Claude accounts the inventory does not list.
Sep 16, 2026 · 6 min read
AI Governance
A Starter Kit for Agents Already in the Building
Founders already have agents running. The first move is smaller than a platform: inventory, ownership, decision records, a defensive tabletop, inbox hygiene, and a privilege matrix before anything acts in production. Six public Grok Bots are that kit.
Sep 15, 2026 · 7 min read
AI Governance
Name the Agent Before It Calls a Tool
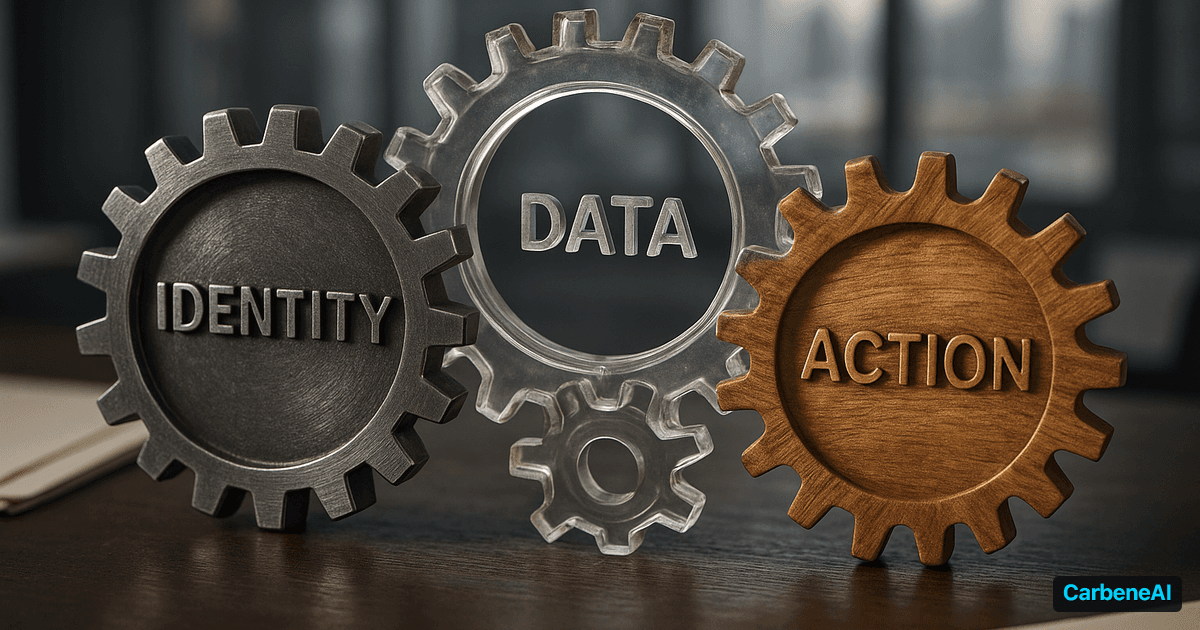
You cannot write an enforceable policy for an agent you have not named. The first move is still one row: identity, data class, allowed actions, the HITL line, a tested stop. I published a Grok Bot that walks you through that row before the agent runs.
Sep 15, 2026 · 7 min read
AI Security
Your Coding Agent's Sandbox Is a Trust Boundary, Not a Convenience
Most teams treat a coding agent's sandbox like a scratch directory. It is a trust boundary. If the agent can reach the host filesystem, the network, or inherited credentials, a sandbox escape is an authentication bug, and it should be patched on that clock.
Sep 15, 2026 · 6 min read
AI Security
The Analyst Is Still the Integration Layer Between EDR, SIEM, and IAM
Each tool does its own job well. The endpoint agent flags the process, the SIEM holds the log, the identity system knows who logged in. Nobody joins them into one incident except the analyst, by hand, at 2 a.m. That manual join is the gap, and it is where response time goes to die.
Sep 15, 2026 · 6 min read
AI Governance
Is This Tool Call Allowed? Answer It at Runtime, Not in a Policy PDF
An agent has made thirty tool calls since you last looked. A policy document cannot tell you whether the thirty-first should run. That decision has to happen at runtime, per call, and it has to leave a record a board can read. The artifact is a decision log, not another GRC binder.
Sep 15, 2026 · 6 min read
AI Governance
The Smallest Artifact That Turns an Ungoverned Agent Into a Governed One
AI agent security is the top concern in the field, twice the size of the next one. The fix is not a platform. It is one row per agent, filled in before it runs: identity, data class, allowed actions, a human-in-the-loop line, and a tested stop.
Sep 14, 2026 · 7 min read
AI Governance
You Can Hire a CISO and Still Have No One Who Owns the Agent
Deloitte's 2026 numbers show 49% of organizations now have a CISO, up from 31% in 2023. Only 11% of those leaders still count legal, compliance, and risk among their top priorities. That gap is where agentic AI goes wrong, and it closes with named owners, not another title.
Sep 14, 2026 · 5 min read
AI Governance
Build the Healthcare AI Audit Trail Before Anyone Asks For It
The demand for an AI audit trail arrives one of three ways: a health-system security review, an OCR inquiry, or your own board. In all three, we log the API calls is not enough. You need a per-inference record, and the vendors who build it first win the review instead of scrambling through it.
Sep 14, 2026 · 6 min read
AI Governance
When AI Answers 911, the Governance Question Is Not Whether, It Is Where
New Orleans put AI on its 911 lines, the press said robots were replacing dispatchers, and the truth sat in between. The real lesson is about where you draw the line between what a machine may decide and what a human must.
Sep 12, 2026 · 6 min read
AI Security
The PaperCut campaign shows how AI can accelerate exploitation
GreyNoise reported 440 compromised PaperCut instances across 395 organizations in an AI-orchestrated campaign. The evidence shows rapid exploitation and privilege escalation, not dwell time collapsing to seconds. Here is what defenders can act on.
Sep 11, 2026 · 6 min read
AI Governance
You Cannot Write a Policy for AI Tools You Have Not Named
A majority of healthcare providers and payers say staff already use unauthorized AI tools, and fewer than 40% have a policy that governs it. The fix is not another all-staff email. It is a first inventory, run as amnesty instead of audit.
Sep 11, 2026 · 7 min read
AI Security
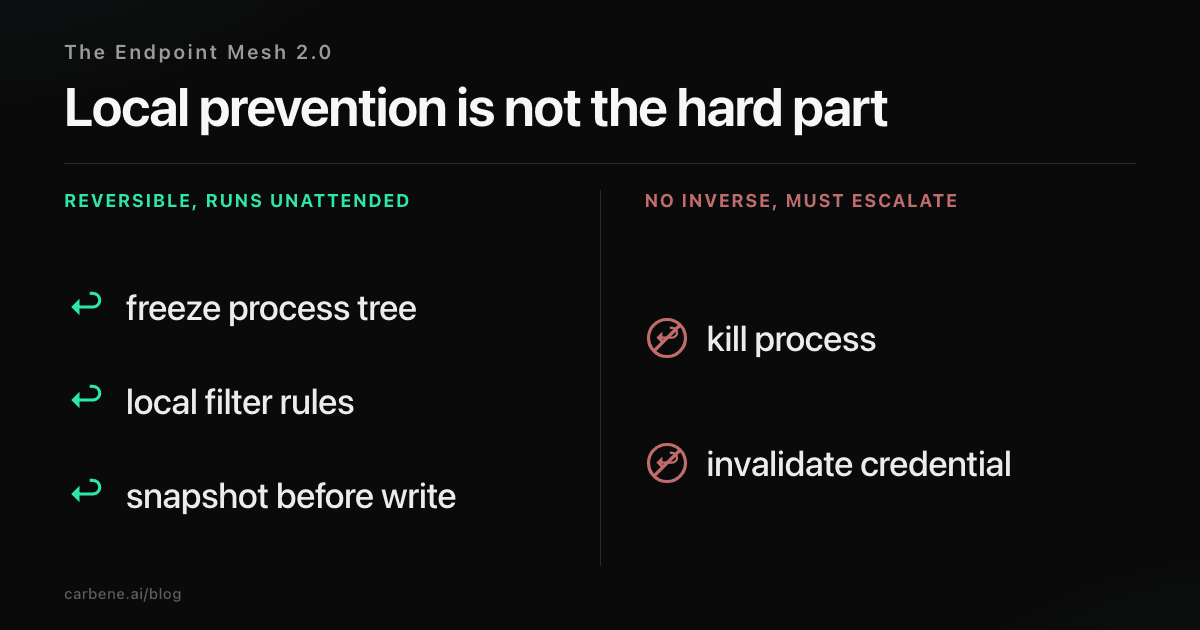
Local Prevention Is Not the Hard Part
Modern EDR already decides on the sensor, so moving the decision to the endpoint is not the interesting problem. The interesting problem is what a fleet of local deciders still cannot do without re-centralizing. Version 2.0 of the Endpoint Mesh is a correction, and the corrections are more useful than the original claims.
Aug 14, 2026 · 18 min read
AI Governance
Your AI Governance Framework Assumes the Model Only Answers
Almost every AI governance framework in circulation is built around a system that produces an output for a person to check. Agents do not do that. When the failure mode moves from a wrong answer to a wrong action, most of the controls you have stop reaching the risk.
Jul 31, 2026 · 13 min read
AI Security
Your SIEM Assumes the Network Is Up
Every SIEM makes two assumptions nobody says out loud: that the endpoint can reach the middle, and that the round trip is fast enough to matter. The second one fails even on a healthy network. Here is what follows when you stop pretending otherwise.
Jul 28, 2026 · 14 min read
AI Security
The Pen Test Your AI Feature Never Got
Every year you pen test your network. The AI feature you shipped last quarter never got the same treatment. Here are the six ways it fails, and how to test for them.
Jul 10, 2026 · 5 min read
AI Governance
We Published Our AI Governance Templates. They Are Free.
Most companies get stuck between a $50,000 assessment and a blank page. So we put the AI governance templates we use on GitHub, free, grounded in NIST AI RMF and ISO 42001.
Jul 7, 2026 · 4 min read
AI Strategy
The Security Review Your AI Feature Has to Pass
A new AI feature can quietly stall your enterprise and agency deals in security review. Here are the decisions that clear it fast.
Jun 24, 2026 · 3 min read
Public Safety
Three Things Public Safety Tech Vendors Get Wrong About Threat Intelligence
Most public safety tech vendor threat intelligence programs are misaligned with what their customers actually need. Three specific mistakes are killing TI program credibility, and the fix for all three is the same.
Jun 5, 2026 · 5 min read
AI Governance
Three Law Enforcement Disciplines That Keep AI in Security Operations Honest
Chain of custody, probable cause, and witness reliability are three law enforcement disciplines that apply directly to AI-augmented security operations. The tooling is new; the instincts that keep you out of trouble are not.
Jun 4, 2026 · 6 min read
Public Safety
CJIS Doesn't Have an AI Chapter Yet. Public Safety Tech Vendors Need One Anyway.
CJIS Security Policy still doesn't have a specific AI section. Public safety tech vendors who keep AI governance separate from CJIS compliance are walking into the next audit blind.
Jun 3, 2026 · 8 min read
AI Security
AI Security Best Practices for 2025
Essential security considerations when deploying AI systems in production environments. Learn how to protect your models and data.
Jan 3, 2025 · 2 min read
Security Research
Understanding LLM Vulnerabilities
A deep dive into common vulnerabilities in Large Language Models and how to mitigate them effectively.
Jan 1, 2025 · 3 min read
AI Engineering
Building Secure AI Pipelines
How to design and implement secure machine learning pipelines for enterprise applications.
Dec 28, 2024 · 4 min read